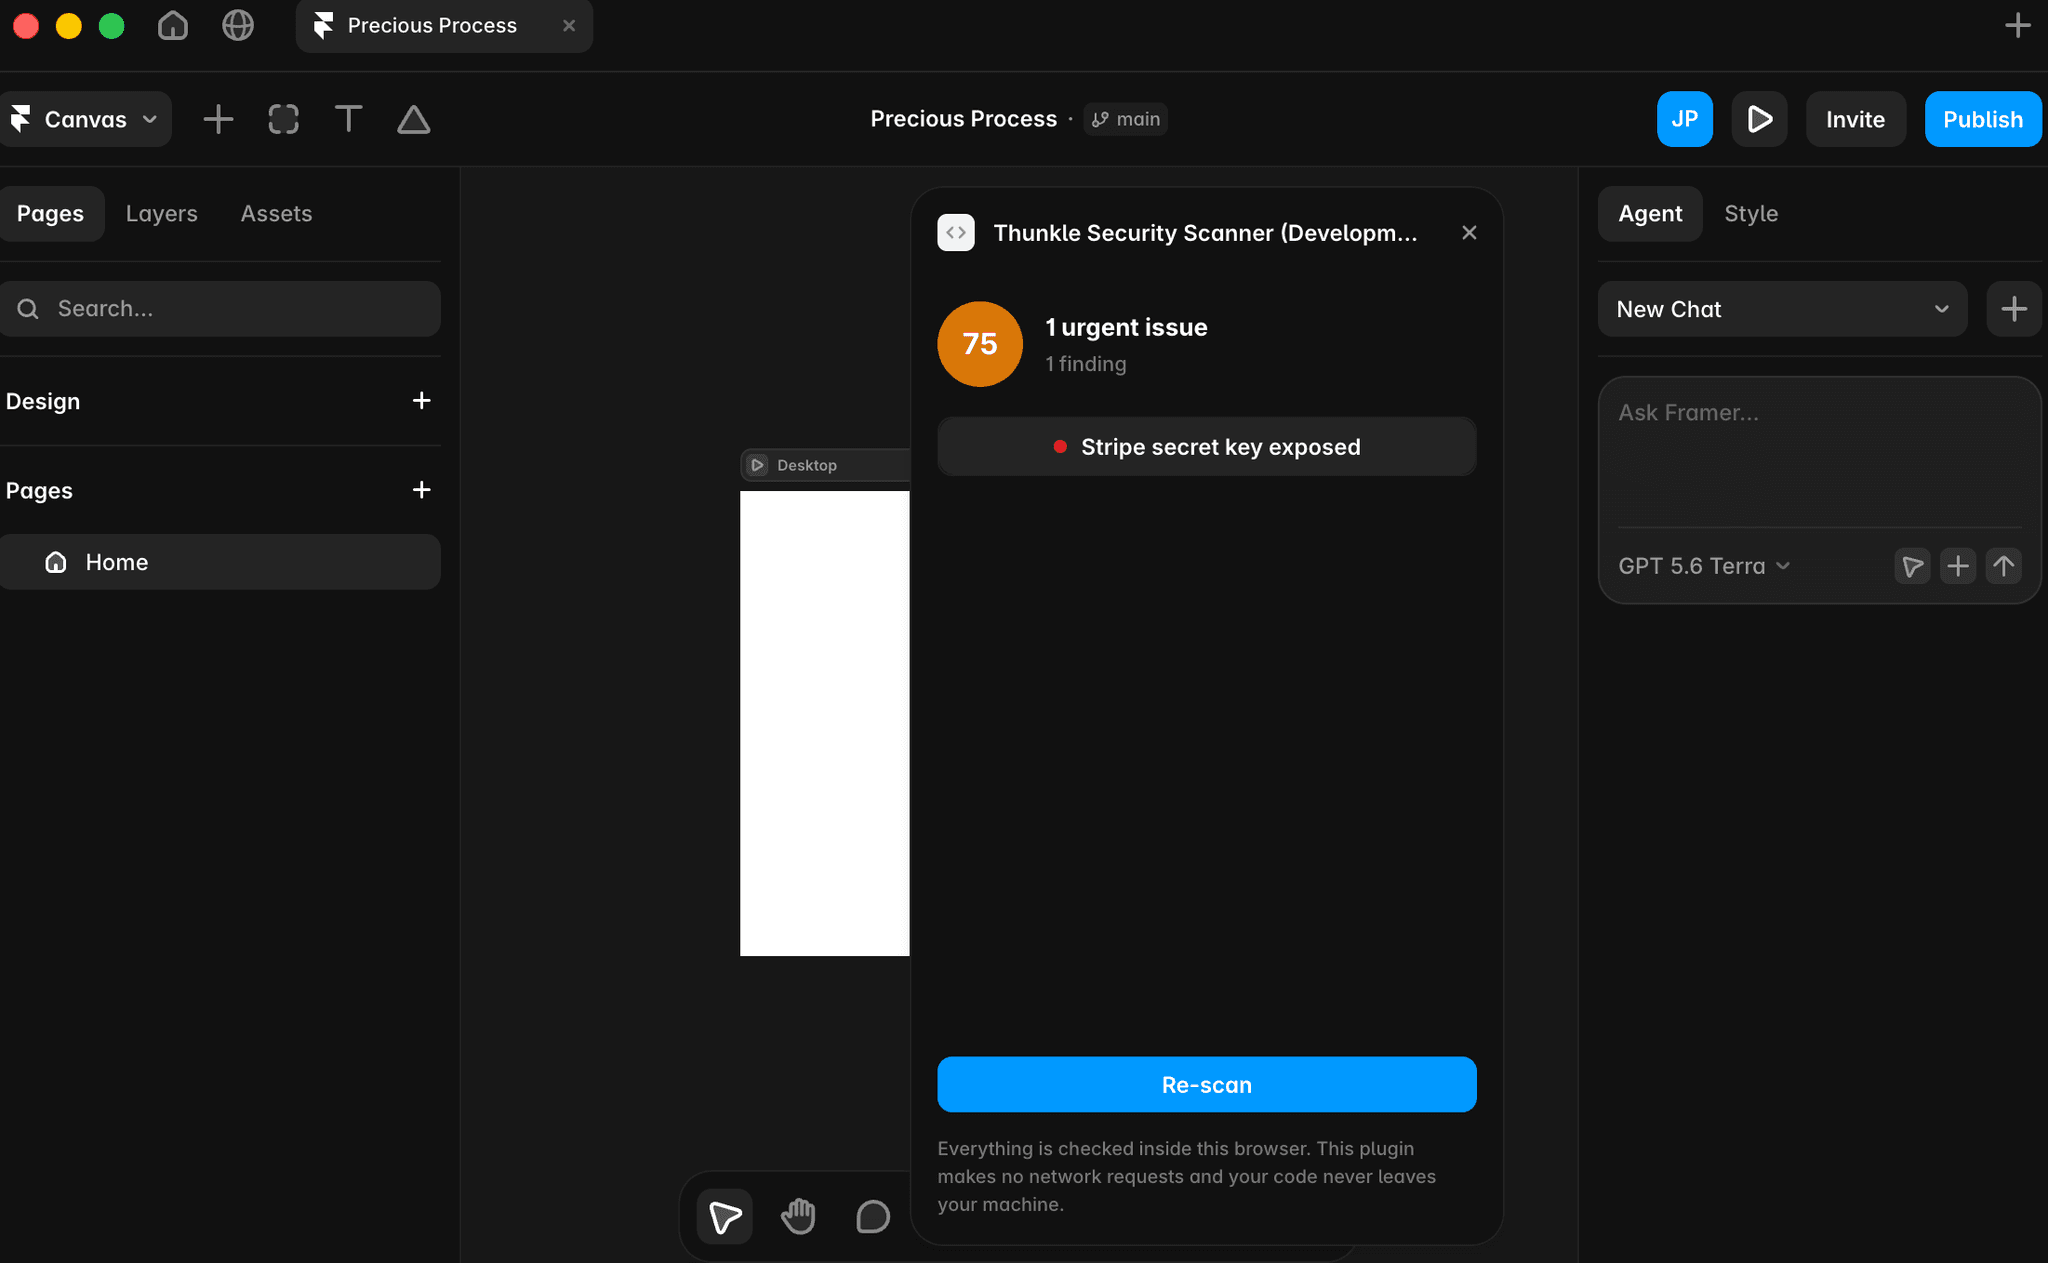
About Thunkle Security Scanner
Checks your code components and redirects for the problems you cannot see from the canvas.
WHAT IT CHECKS
• Exposed credentials. API keys and tokens hardcoded into your code components, where anyone can read them in the published bundle. Covers Stripe, AWS, OpenAI, Anthropic, Supabase, GitHub, Groq, Replicate, Hugging Face, Perplexity, Resend, Convex, SendGrid, Slack and Twilio.
• Redirects. Chains that hop twice before landing, loops that error out, duplicates fighting over the same path, and redirects pointing at pages you have since deleted. None of this is visible in Framer's redirect list, and after a site migration it is usually a mess.
• Imported code. Framer lets a component import straight from a URL, which means whoever controls that host controls part of your site. Anything loaded over http, or from a CDN we do not recognise, gets flagged. Normal imports from esm.sh, jsDelivr, unpkg and Skypack stay quiet.
• Unsafe patterns. dangerouslySetInnerHTML, eval and new Function, and credentials read out of the page URL, where they leak into browser history, referrer headers and analytics.
• Insecure requests. fetch and axios calls to http addresses, which travel unencrypted and get blocked on an https site.
KNOWS THE DIFFERENCE
Firebase browser keys and Supabase anon keys look exactly like secrets but are public by design. Most scanners flag them, panic you, and lose your trust. This one reads the JWT and tells service_role from anon, so a finding here means something.
PRIVACY
Everything runs inside your browser. This plugin makes zero network requests: no accounts, no telemetry, no uploads. Your code never leaves your machine. It is a small static bundle, so open devtools and check.
PRICING
Free. Every check, no tiers, no licence key, no upsell.
WHO MADE IT
Built by Thunkle, who do security and code audits for AI-built and no-code apps. https://thunkle.ai
SUPPORT
Questions, false positives, feature requests: jacob@thunkle.ai